In the traditional enterprise world, data privacy and compliance have always relied on a fragile foundation: legal contracts, policy framework promises, and trusted third-party intermediaries. You send over your data, sign an NDA, and hope the other party sticks to the rules.
In the age of distributed computing, high-frequency cyber threats, and quantum risks, that system is no longer sufficient.
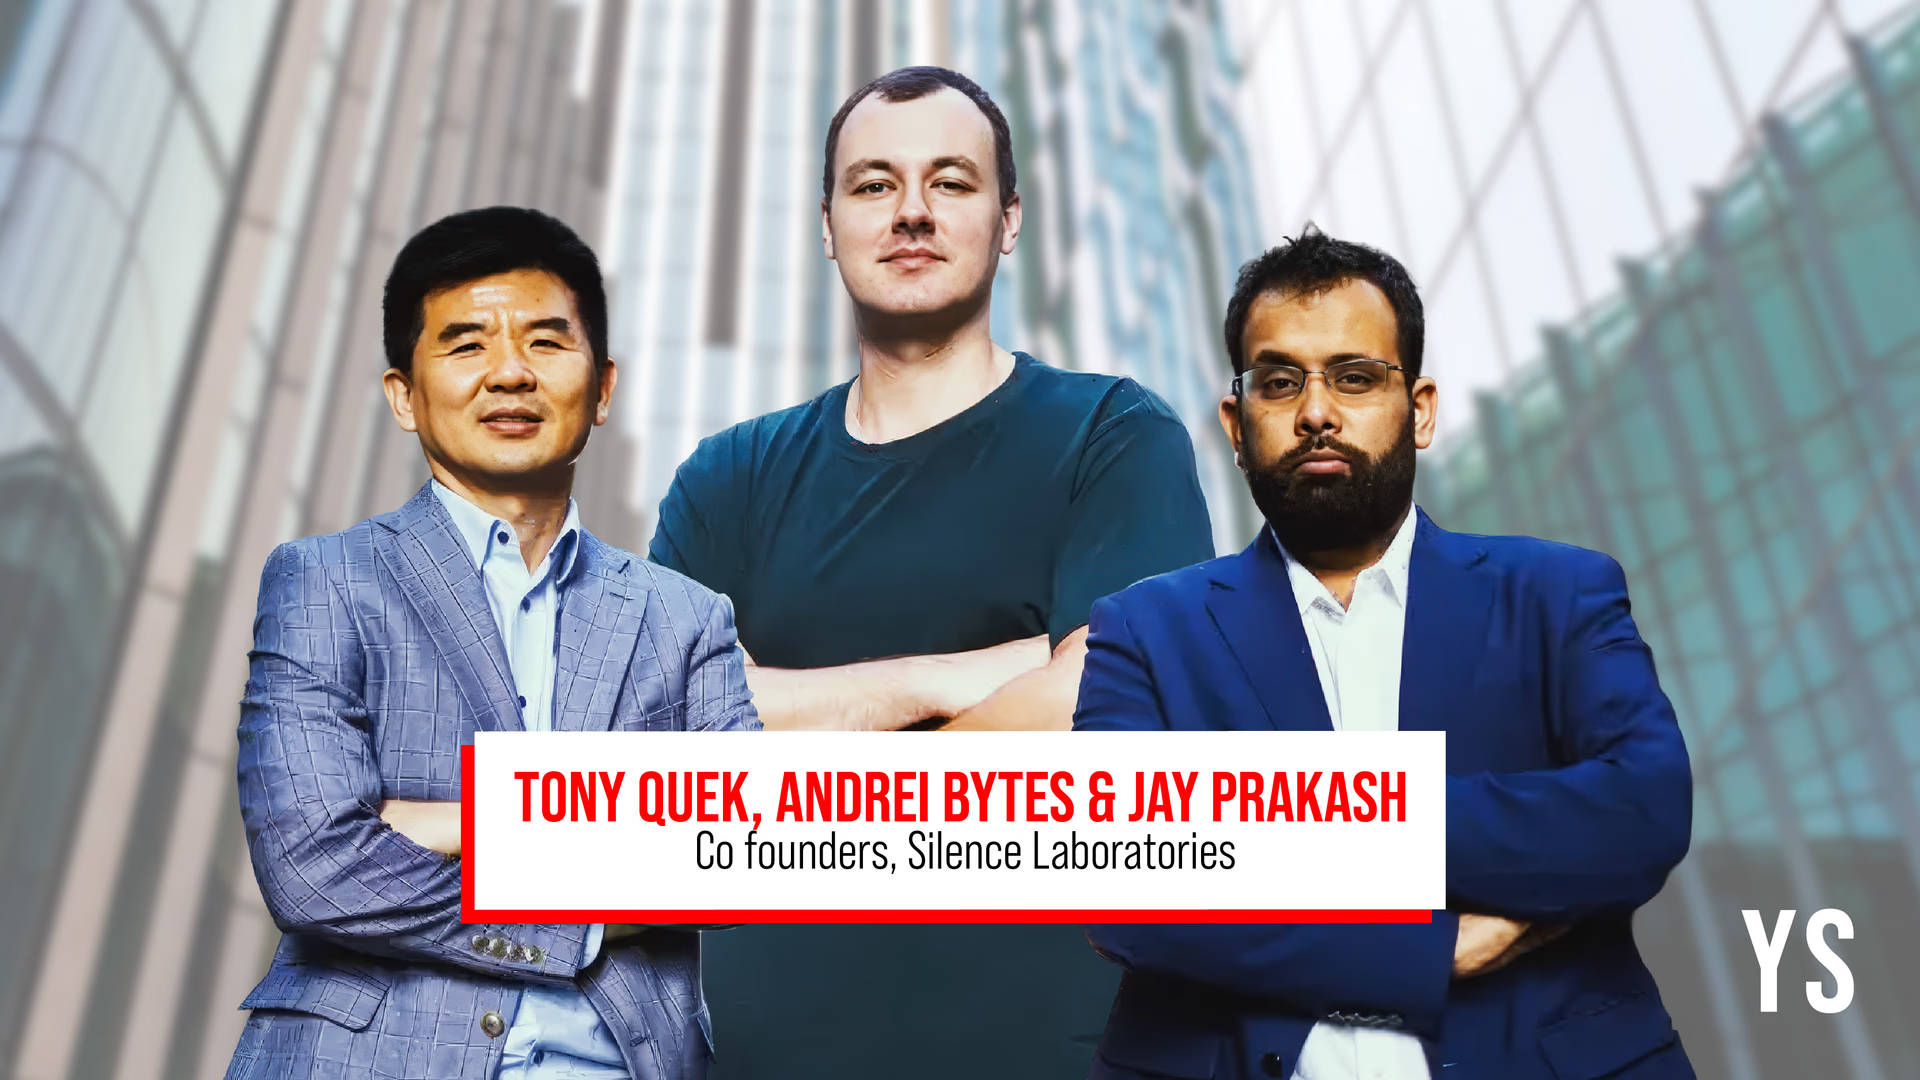
Palo Alto-based cybersecurity startup Silence Laboratories is pioneering a paradigm shift that replaces institutional trust with cryptographic mathematics. Founded by Jay Prakash (CEO), Andrei Byte (CTO), and Tony Quick (CMO), the 30-member research-driven team spans 14 countries and builds privacy-preserving infrastructure that allows organizations to compute over encrypted, distributed data sources without ever exposing raw information.
Here is my breakdown of how Silence Laboratories is taking academic cryptography out of the lab and into mainstream enterprise environments, and why post-quantum readiness is becoming non-negotiable.
1. The Core Innovation: Cryptographic Computation Virtual Machine (CCVM)
Traditional data sharing requires organizations to unencrypt sensitive information to analyze or compute it—creating a massive vulnerability window.
In contrast, Silence Laboratories solves this problem through its Cryptographic Computation Virtual Machine (CCVM), which leverages two core cryptographic frameworks:
- Multi-Party Computation (MPC): Enables multiple entities to jointly compute shared insights over distributed data sources without revealing their private input values to each other.
- Zero-Knowledge Proofs (ZKP): Allows one party to mathematically prove a statement is true without revealing the underlying sensitive data behind it.
Under the traditional approach, raw data is sent to unencrypted cloud environments, relying on policy audits and trust. Under the CCVM approach, encrypted data is processed directly through a mathematical MPC and ZKP engine to deliver instant outputs without raw data ever leaving organizational boundaries. Companies no longer have to worry about third-party data leaks or compliance violations during joint analytics.
2. Real-World Execution: From Big Banks to Global Tech Sprints
While technologies like MPC and ZKP have existed in academic papers for decades, the real engineering hurdle is performance, scalability, and seamless deployment.
Silence Laboratories currently serves over 35 global clients across banking, custody, fintech, and digital assets:
- International Banking: Partnerships include a Top-4 US bank, along with participation in the Bank for International Settlements (BIS) Project Mandala for cross-border compliance.
- Global Recognition: Won the 2025 G20 TechSprint alongside Proxtera for cross-border credit data portability, and secured top honors in the 2026 Accenture Technology Next Challenge for cybersecurity.
- Fintech & Web3 Infrastructure: Core security design partnerships and deployments with BitGo, MetaMask, Fold, Finvu, Biconomy, Okto, Zengo, and EigenLabs.
- Open Source Commitment: Open-sourced parts of its Agentic Privacy-Preserving Protocol (AP3) via the Linux Foundation Decentralized Trust.
Blogger’s Insight: The fact that both traditional banking giants and Web3 custody platforms are adopting the same underlying MPC infrastructure shows that privacy-preserving computation is fast becoming the universal standard for enterprise data exchange.
3. Preparing for the Quantum Threat Horizon
Most modern digital signature schemes are vulnerable to future quantum computing decryption capabilities. For financial institutions and digital asset custodians holding billions in assets, waiting for quantum computers to arrive before updating encryption standards is a recipe for disaster.
To address this, Silence Laboratories introduced Post-Quantum MPC Protocols built on ML-DSA (FIPS 204), the digital signature standard recognized by the National Institute of Standards and Technology (NIST).
In a milestone simulation alongside digital asset custodian BitGo, the team completed the first post-quantum MPC transaction simulation for regulated custodians—proving that enterprise entities can seamlessly upgrade to quantum-safe security without dismantling existing wallet or key-management workflows.
4. Closing the Awareness and Regulatory Gap
Despite the maturation of privacy-enhancing technologies, broad adoption faces two primary hurdles:
- The Perception Gap: Many enterprise executives still incorrectly assume that privacy-preserving computation is too slow, resource-intensive, or unready for production workloads.
- Regulatory Lag: Jurisdictional policies continue to focus on post-facto data regulation rather than mandating cryptographic privacy guarantees at the infrastructure layer.
As Privacy-Enhancing Technologies (PETs) become easier to integrate, privacy should no longer be viewed as a costly regulatory burden—it is a strategic growth enabler that unlocks cross-organizational data partnerships previously blocked by legal departments.
Final Thoughts: The Shift to Mathematical Security
The future of network security isn’t about building taller walls around your databases; it is about ensuring that even if someone gains access to the pipeline, the data remains mathematically unreadable and fully under your control.
Organizations that embrace zero-knowledge proofs and post-quantum MPC today will not only protect themselves against future threat landscapes—they will lead the next wave of secure, cross-border digital collaboration.
What’s Your Perspective?
Is your organization exploring privacy-enhancing technologies like MPC or Zero-Knowledge Proofs for cross-team data analysis? Or are legacy compliance policies still slowing down adoption in your industry? Let’s discuss in the comments below!